Unified AI Governance. Full Lifecycle. One Platform.
Register, govern, score risk, and trace dependencies across every AI agent, model, and MCP server — on a platform that governs your entire technology estate.
Not ready to talk? Score your governance maturity in five minutes, free and without signing up.
- Governed entity types
- 8
- Built-in frameworks
- 13
- Dependency layers traced
- 6
Engineered for enterprise trust and compliance
- EU AI Act
- NIST AI RMF
- ISO/IEC 42001
- AWS Cloud
- Docker Self-Hosted
- Hybrid Deployment
- SOC 2 Certification in Progress
- Your Data Kept Private & Separate
Know what you've built
One registry for every AI system, and everything it runs on
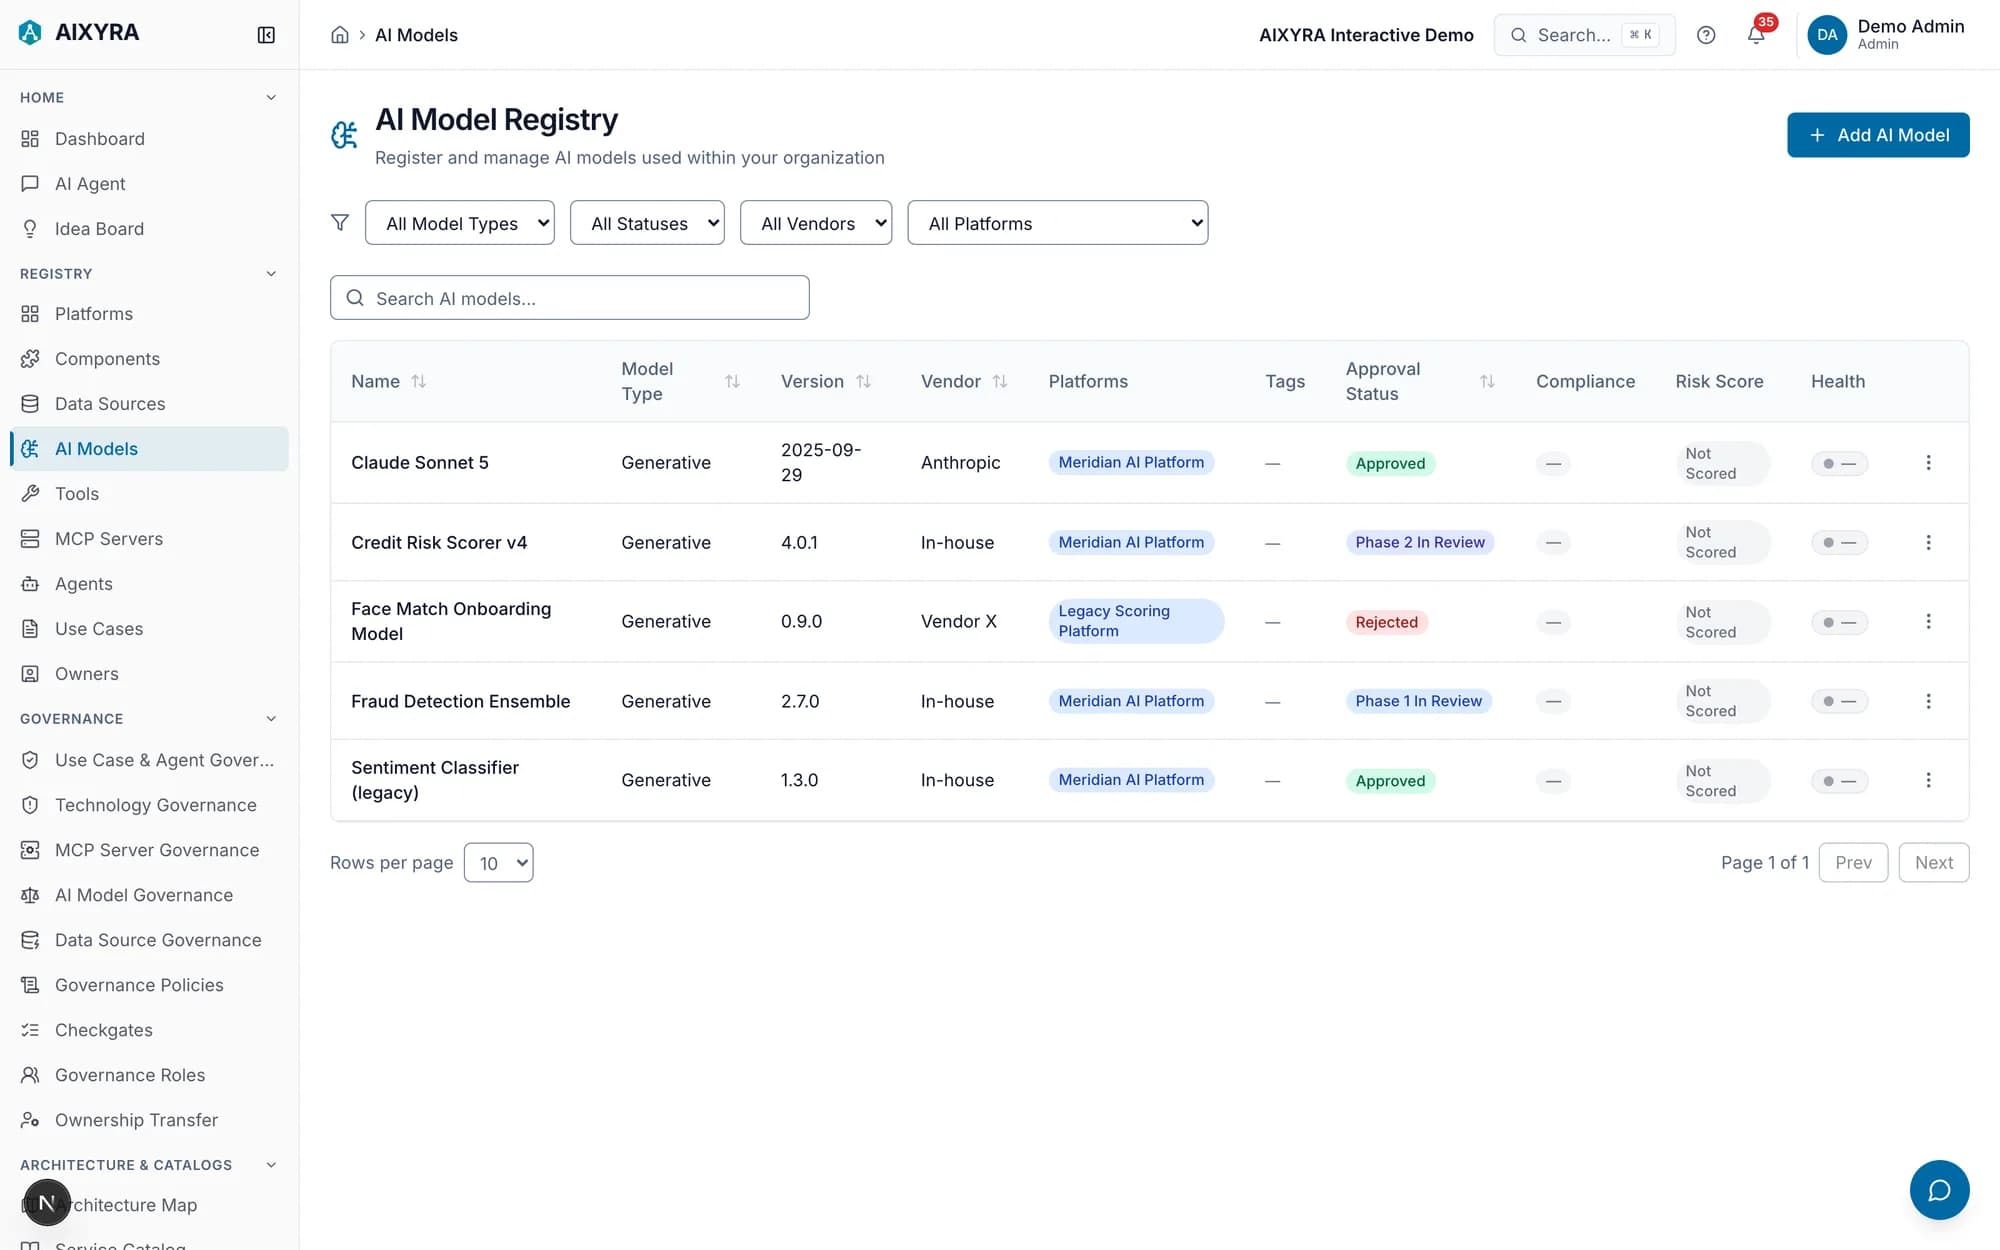
Agents, models, MCP servers and use cases, alongside the tools, data sources, platforms and components they depend on. Register them, or let AIXYRA find the ones already running in your cloud accounts and model providers and bring them under management.
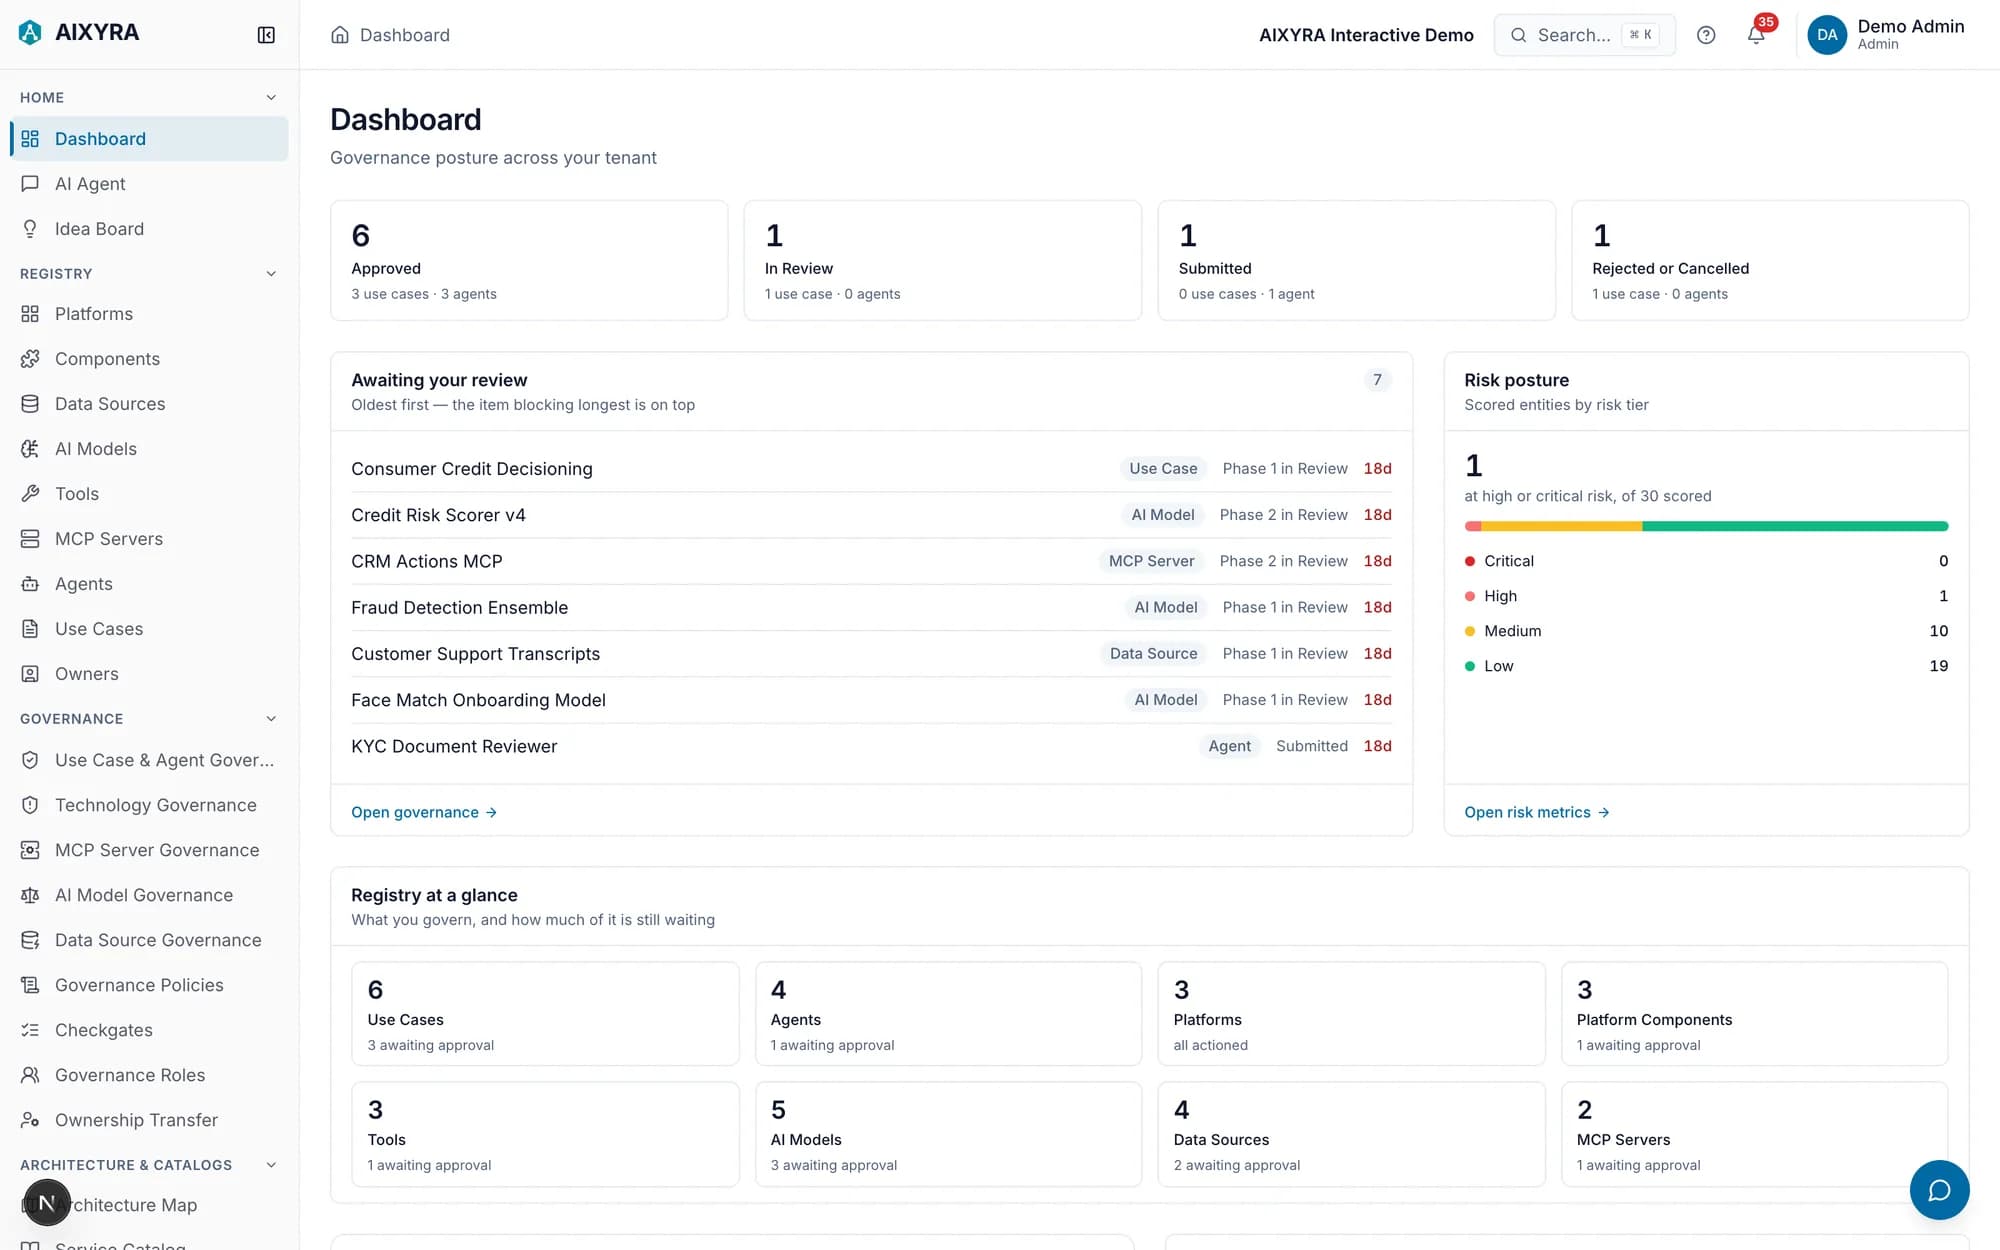
- Eight governed entity types in one registry, not eight tools
- Shadow AI discovery across AWS, Azure and Google Cloud
- Ownership, lifecycle stage and classification on every record
AI-first
- AI Agents
- Models
- MCP Servers
- Use Cases
Technology estate
- Tools
- Data Sources
- Platforms
- Platform Components
Govern before you deploy
A review that happens on the way to production, not after it
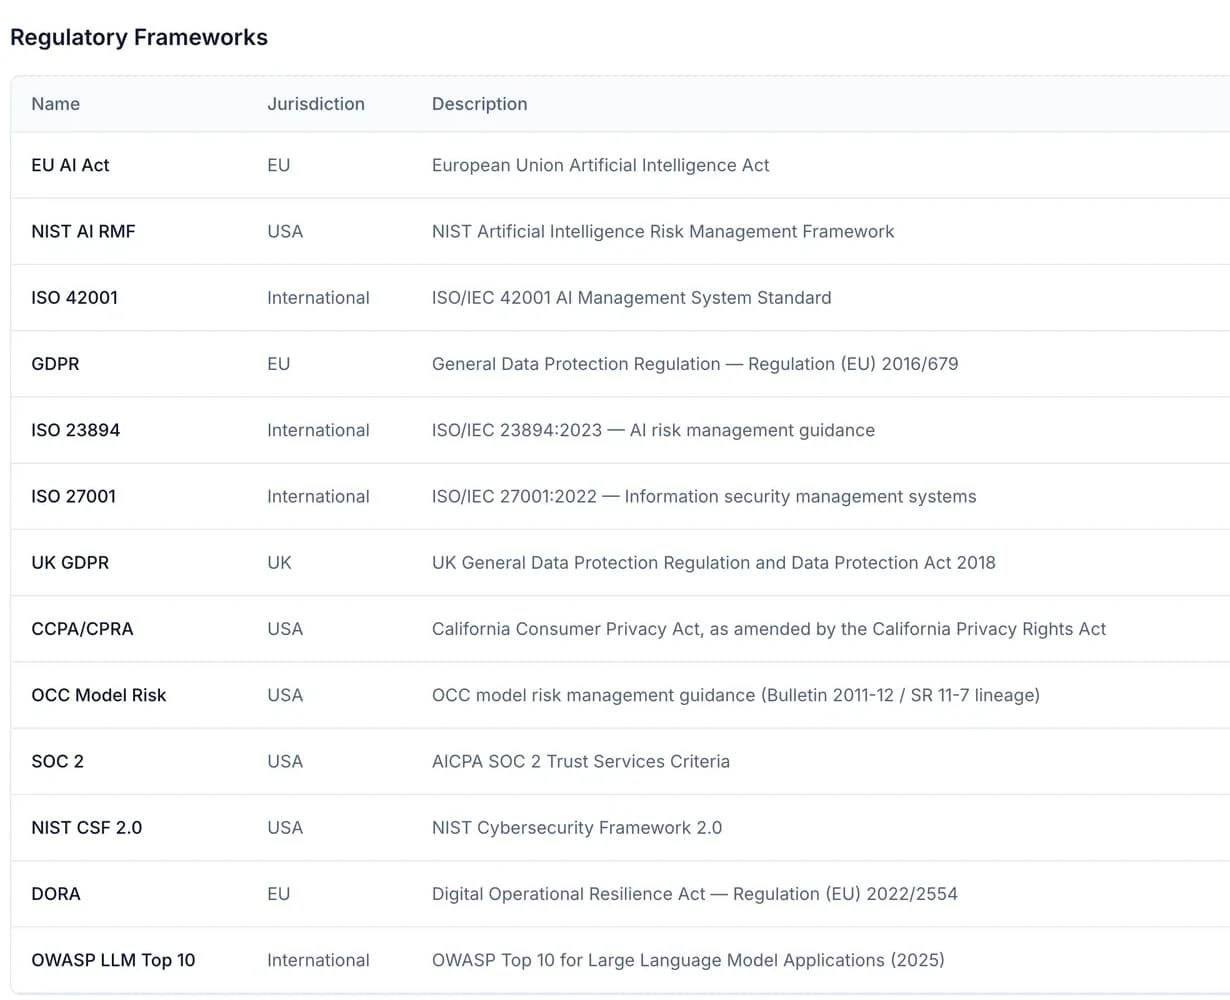
Two-phase approval with configurable checkgates and named reviewers. Work in flight is visible to whoever has to sign it off, and a governance gate in your pipeline can stop an artifact that has not cleared its phase.
- Fit for Purpose and Fit for Use, with the checkgates you define
- A review queue that shows what has been waiting longest
- A GitHub Action that fails the build on ungoverned deployments
Comply with confidence
Map an AI system once, and the evidence serves every framework
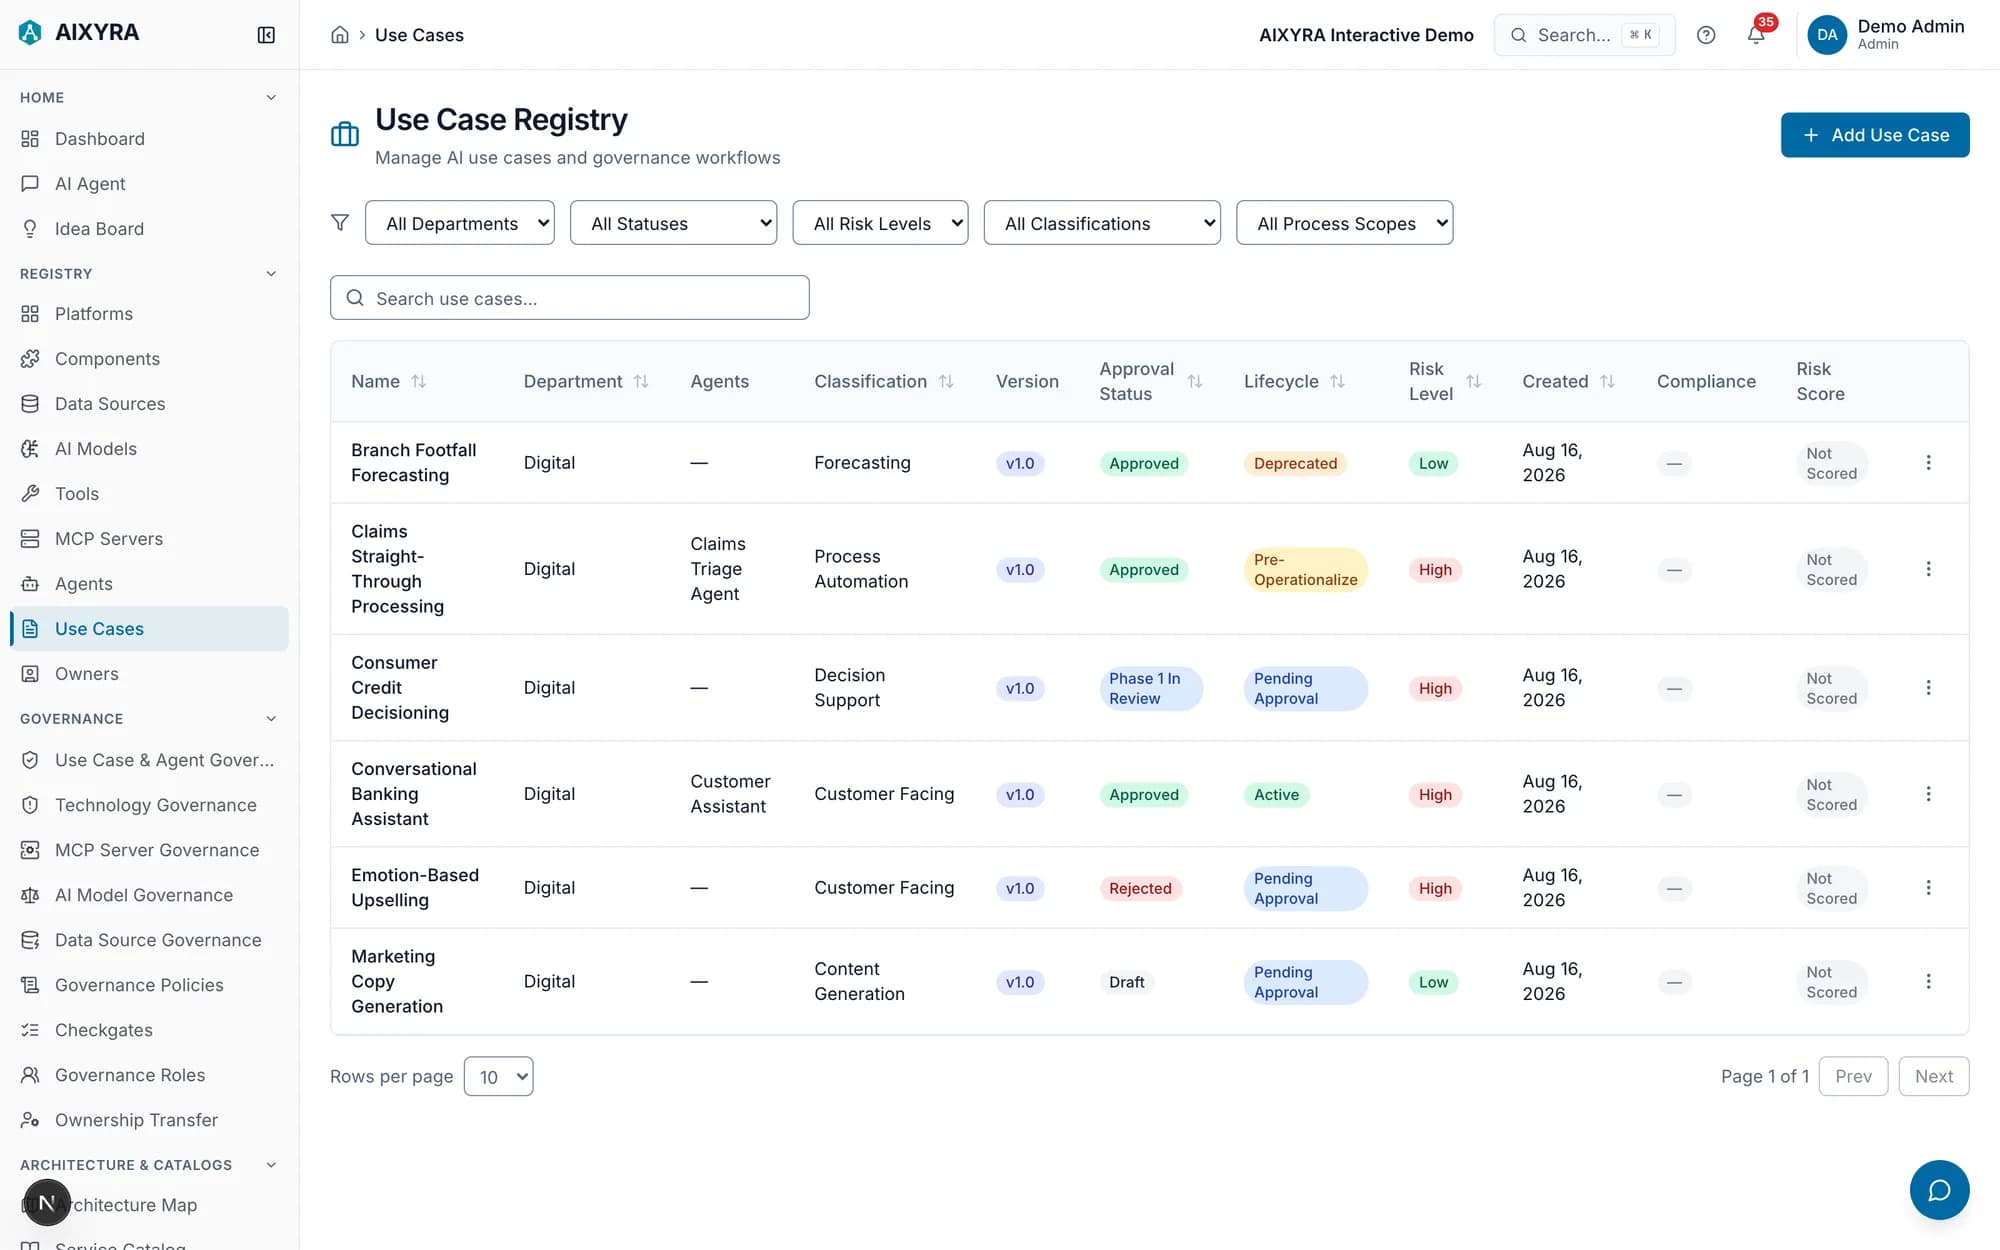
Thirteen frameworks ship built in, down to the individual requirement: more than 650 articles, clauses and controls, seeded and assessable. Obligations attach to individual systems rather than living in a binder, so coverage is a property of the estate and audit evidence is generated rather than assembled.
- All 113 articles of the EU AI Act, and all 99 of the GDPR
- Thirteen frameworks across AI, privacy, security and financial services
- Custom frameworks built from the articles that apply to you
- An append-only audit trail, and model cards for Article 13
See how every AI system connects — and how risk cascades
Most tools govern AI systems in isolation. AIXYRA maps the full six-layer dependency chain, so you can trace how every agent, model, tool, and data source connects to the platforms and services beneath it.
Dependencies flow down. Understand exactly what each AI system relies on, end to end.
Risk propagates up. A change or vulnerability deep in the stack surfaces on every system that depends on it.
One governed estate. AI entities and the technology that runs them, in a single dependency graph.
How mature is your AI governance?
Get a readiness score across six governance dimensions, see your clearest gaps, and walk away with a report you can put in front of your leadership. Optionally extend it to your broader technology estate.
- Twenty questions, under five minutes
- Instant scored report with recommendations, as a page, PDF, or email
- No signup, and your answers never leave your browser
Frequently Asked Questions
What is AI governance and why does it matter?
AI governance is the framework of policies, processes, and controls that ensure AI systems are developed, deployed, and operated responsibly. With 86% of organizations reporting at least one AI-related security incident in the past 12 months (Cisco, 2025) and only 43% having a formal AI governance policy (PEX Report, 2025), the urgency for structured governance has never been greater. Regulations like the EU AI Act impose penalties of up to EUR 35 million or 7% of global turnover for non-compliance.
What is AIXYRA?
AIXYRA is a unified full-lifecycle AI governance platform that enables organizations to register, govern, assess compliance, score risk, and trace dependencies across every AI system — from a single platform. It covers 38 capabilities across 7 categories including AI Agent Registry, AI Model Catalog, MCP Server Registry, Shadow AI Discovery, Compliance Frameworks, Risk Scoring with Dependency Propagation, CI/CD Governance Gate, AI Model Card Generation, Continuous Governance & Health Monitoring, Architecture Dependency Graphs, Architecture-as-Code, Policy-as-Code Validation with OPA and Rego, and a private AI Governance Agent.
Which regulatory frameworks does AIXYRA support?
AIXYRA supports 13 built-in compliance frameworks — EU AI Act, NIST AI RMF, ISO/IEC 42001, GDPR, UK GDPR, CCPA/CPRA, ISO/IEC 23894, ISO/IEC 27001, NIST CSF 2.0, SOC 2, DORA, OCC Model Risk Management, OWASP LLM Top 10 — plus custom frameworks you define. For the EU AI Act, high-risk obligations apply from December 2, 2027, following the Digital Omnibus postponement under Regulation (EU) 2026/1744. The platform enables organizations to map their AI systems against these frameworks simultaneously and demonstrate compliance through automated assessments and governance workflows.
How does AIXYRA address the agentic AI governance challenge?
With 62% of organizations experimenting with AI agents (McKinsey, 2025) but only 21% having mature governance frameworks for agentic AI (Deloitte, 2026), AIXYRA governs the agentic era directly. This includes MCP Server Registry with approval workflows, configurable governance checkgates, and architecture dependency graphs that trace relationships across agents, models, tools, data sources, platforms, and services.
What types of organizations benefit from AIXYRA?
AIXYRA serves government and defense organizations requiring data sovereignty, financial services needing model risk management, healthcare organizations with clinical AI validation requirements, technology companies managing governance at engineering velocity, consulting firms managing governance across many clients, and regulated industries facing EU AI Act compliance deadlines.
Ready to Govern Your AI with Confidence?
Join forward-thinking organizations that are building responsible AI governance frameworks today. Get started with a personalized demo.